Verisign used Sitefinder to distribute Spyware?
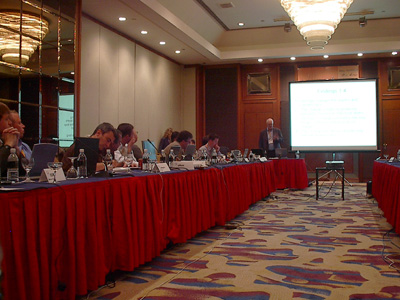 Steve Crocker, chair of ICANN Security and Stability Advisory Committee, today briefed the Registrar Constituency on their recent report on Sitefinder. One of the points in Steve's slides floored me.
Apparently, Verisign used the Sitefinder to distribute software to end-user desktops without their knowledge or consent. Digging into the SSAC report a bit deeper, I came across this little gem...
 "Analysis of Site Finder revealed that a "web bug" had been embedded in the page so
 that information about the behavior of users of the page was sent to a company named Omniture, which monitors Web traffic. Information about users of Site Finder was passed off to a third party, again without the consent of the users and perhaps without their knowledge."
I'm utterly stunned.
The Omniture web page boasts a slogan - "Unique questions, precise answers." Here's my unique question - is this appropriate behavior for the custodian of the community resource?
See this post as it first appeared on Blogware.
2 comments
Comments are closed - these are kept exactly as they were left.
(name not saved), July 19, 2004
Folks know I'm no fan of VeriSign, but they certainly did not distribute Spyware. I think Ross is confusing a "web bug" (which is typically a snippet of Javascript or a clear pixel, that allows a 3rd party site to receive a "hit" for statistics, etc) with the "Weather Bug" (www.weatherbug.com) or other EXECUTABLE programs. The web bug would be only in the browser itself, on the relevant pages of Sitefinder, and wouldn't be installed on the desktop, or as a browser "enhancement".
Of course, VeriSign would have had the potential to put more aggressive marketing (including true Spyware) onto Sitefinder, had they been allowed to keep it running.
(name not saved), July 19, 2004
I'm well aware of the differences between spyware, cookies, etc...
The real explanation has to come from Verisign, not from me. I'm just relating what the SSAC slides and report said - the slides specifically said "spyware". In any event, the mechanics aren't really all that important, are they?
The fact remains, it seems, that Verisign abused the public in ways that we're only now really becoming aware of - and that's just plain wrong.