Phishing for better URLs
I was surprised to notice the URL that CIBC is using for their online banking – it seems like great bait for a phishing attack.

Using a fourth-level domain www.cibconline.cibc.com instead of the simpler for, cibc.com or www.cibc.com makes it really easy for the bad guys to fool people into clicking links that look like this:

Note that I changed the root domain in the URL from cibconline.cibc.com to cibccom.co – a fairly innocuous domain that is available for registration today, and therefore fair game for a bad guy to start using tomorrow.
It is trivial nowadays to show users friendly URLs, no matter how complicated your backend is. I’d really love to see CIBC use something like this:
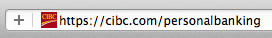
While it won’t completely solve the phishing problem, it will make their banking app a little more friendly and easier for an average user to understand the difference between a fake URL coming from a bad guy and the real one coming from their bank.
See this post as it first appeared on WordPress.
3 comments
Comments are closed - these are kept exactly as they were left.
Michele Neylon, October 3, 2011
Banks never cease to amaze me when it comes to stupidity. They know they're targets for phishing attacks yet, as you've pointed out, they almost help the phishers.
In Ireland most of the banks don't even publish SPF records, so the phishers can easily forge their email domains
Ross Rader, October 3, 2011
Yeah, in a lot of cases they do. Unfortunately, a lot of the blowback lands in our laps as we have to cleanup from the false accounts, illegitimate registrations and credit card chargebacks.
Michele Neylon, October 4, 2011
Same here :(